Independent Engineer · AI, Infrastructure & Security

AI systems
on solid
infrastructure.

I design and build AI and agent systems, reproducible Linux and NixOS infrastructure, and the network and security layers around them, for developer teams, startups and anyone working on hard technical problems.

Scoped projects. Hourly support. Part of your team.

Based in Vienna · Remote worldwide· On-site in Vienna

Tim Witter
Tim WitterIndependent engineer
ENGINEERING ACROSS THE LAYERS

How I can help

Agents on top.
Infrastructure underneath.

I work where software meets the machine: agents that run safely, hosts that can be rebuilt from a file, and networks that only allow what they should. That might mean building something new, hardening an existing system, or making it easier to operate.

AI & agent systems

I build AI systems, LLM integrations and agent workflows with the boundaries they need: isolated execution, scoped tool access, controlled egress and clear ownership of credentials. The aim is agents you can operate, audit and trust.

Agent workflows · Isolated runtimes · Tool & model gateways

Linux & NixOS infrastructure

Declarative hosts, reproducible environments, and MicroVM or container isolation. I replace hand-built servers with configuration that a team can review, rebuild and roll back.

NixOS hosts & flakes · MicroVMs & containers · Automation

Network & security

Segmentation, egress control, secrets handling and access policy, backed by a written threat model. I design for the failure you expect rather than the one you hope to avoid.

Threat models · Egress & segmentation · Secrets & access

Software & tooling

Command-line tools, services, terminal UIs and APIs in Rust, Go and Python: software that operates systems rather than decorates them. Web interfaces when they serve that system, such as a dashboard.

CLIs & services · Terminal UIs · APIs & integrations

What I’m building

Tentaflake.
Agents that keep running, declared with NixOS.

My current open-source work: a NixOS tool that keeps AI agents running around the clock on a headless Linux machine. Each agent lives in its own isolated container, declared in a flake, and Tentaflake is the environment around them all.

DECLARATIVE

A NixOS flake

Hosts, agents and their runtimes are configuration you can review, rebuild and roll back.

ISOLATED

A capsule per agent

Each agent runs in its own container with its own secrets, skills and persistent workspace. By default it has no direct network access; models and the web are reached through policy.

ALWAYS ON

Headless, 24/7

Declare an agent once and it runs on a Linux box with no desktop session. systemd restarts it after a crash, and unattended start requires its policy boundaries to be in place.

The agents in the background

  • Hermes supported
  • ZeroClaw supported
  • OpenClaw scaffold only

An illustration of agents at work in a Tentaflake environment, not a live view.

OPEN SOURCE Pre-1.0 and under active development: interfaces and defaults may still change.

Ways to work together

A clear scope.
A practical way forward.

Bring me a defined project, a specific problem, or a role within your team, whether you are a developer team, a startup or one person building something technically demanding. We agree on responsibilities, priorities, and a way of working.

A DEFINED OUTCOME

Project delivery

I work from an agreed scope and milestones through implementation and handover, with clear communication about progress and technical decisions.

FOCUSED HELP

Hourly support

I help with targeted implementation, debugging, integrations, and improvements when you need engineering support for a specific piece of work.

PART OF YOUR TEAM

Embedded contracting

I join your existing workflow, use your tools and conventions, and take ownership of agreed responsibilities alongside your engineers.

About & approach

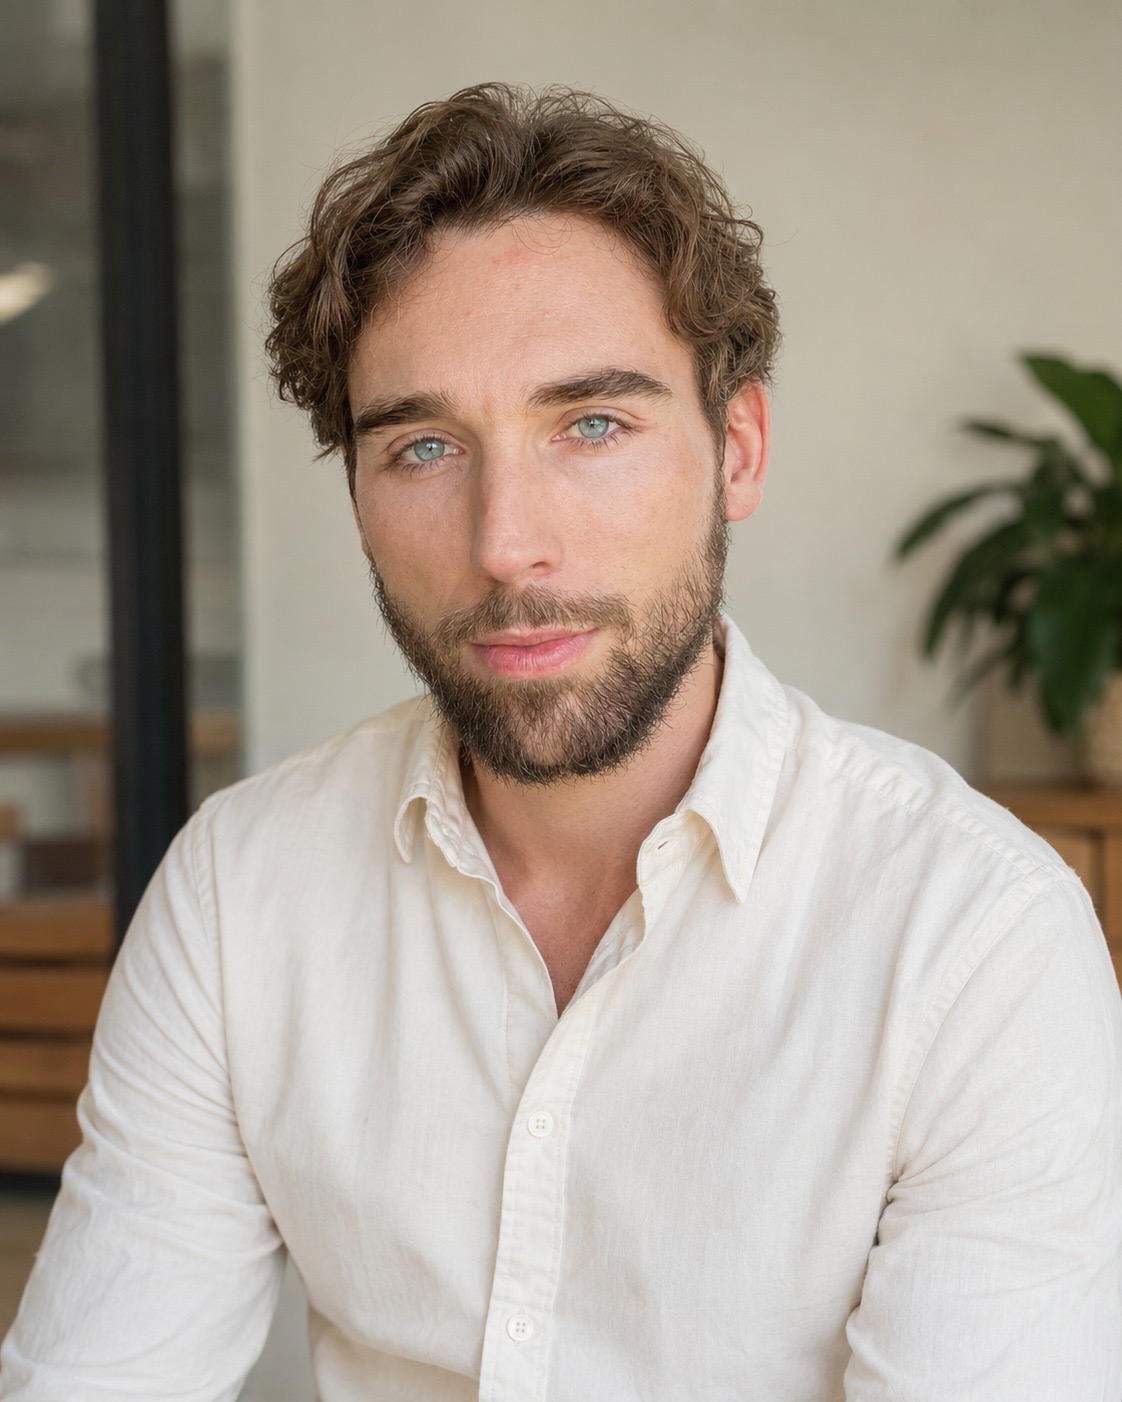
Hi, I’m Tim.
I like the whole picture.

I’m an independent engineer based in Vienna. I like systems with clear boundaries: where an agent may act, what a host may trust, what a network should allow.

I start by understanding the requirements, the existing code, and the people working with it. I explain trade-offs, make decisions in context, and aim for software that remains understandable after handover.

I’m comfortable owning a defined piece of work and collaborating with the team around it. The tools depend on the problem; maintainability and clear communication stay part of the process.

A good fit: developer teams, startups and individuals building technically demanding systems, such as agent platforms, infrastructure, and network or security tooling. A weaker fit: generic SaaS products that are likely to be commoditised within months. I will say so early.
TOOLS I WORK WITH

Rust / Go / Python /TypeScript / Bash
Linux / NixOS/systemd / Tailscale

Have something in mind?

Let’s talk about
what you’re building.

Ask a technical question

Or copy my address into your email app: hello@timwitter.com

For a project, tell me what you need, your expected timeline, and whether you prefer a scoped project, hourly support, or work with your team. For a technical question, a short description and relevant context are enough.